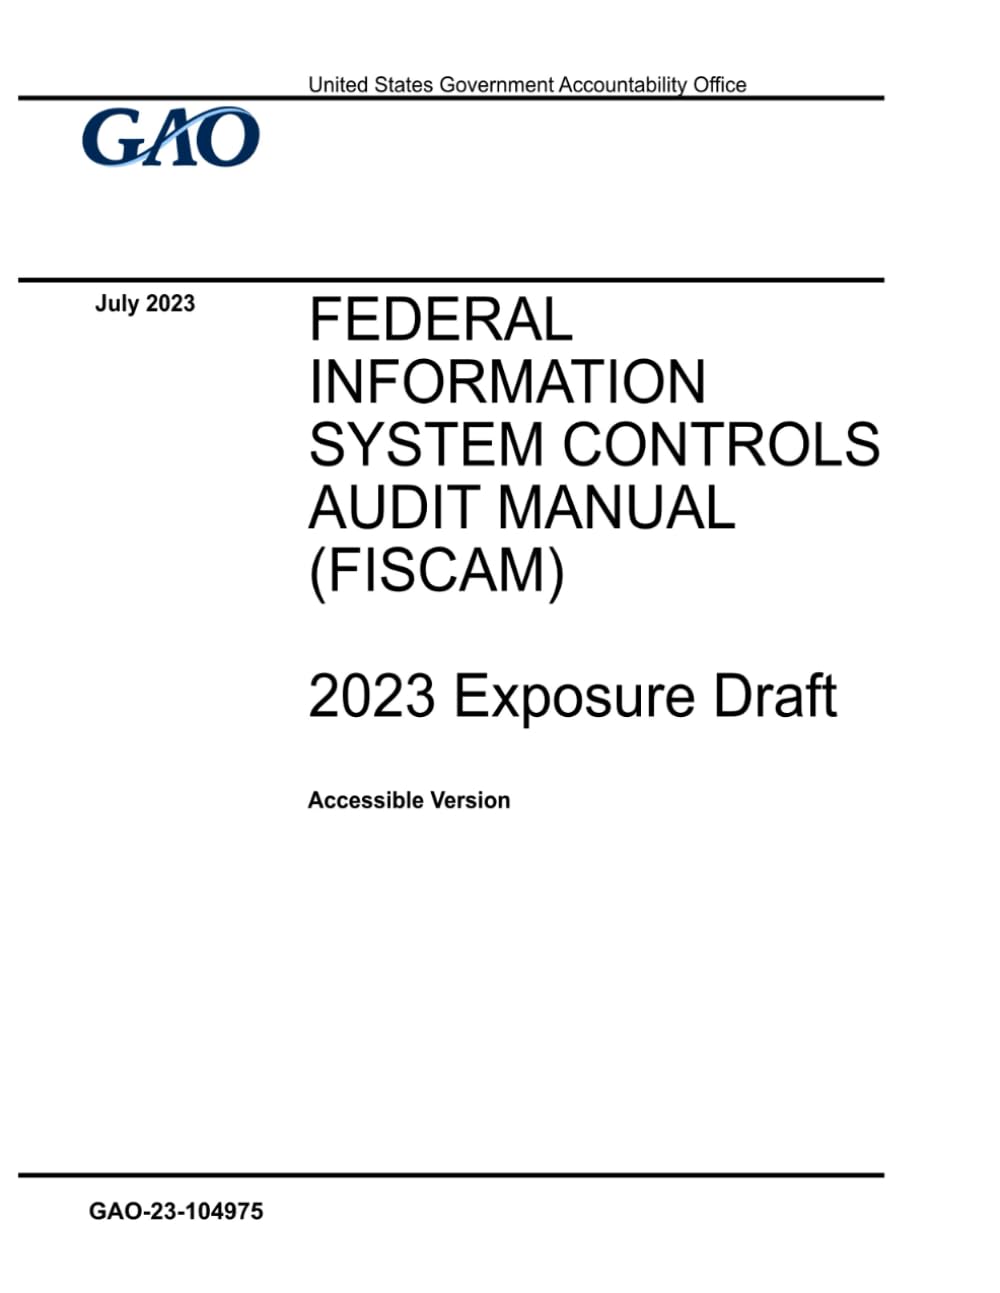
Federal Information System Controls Audit Manual (FISCAM): 2023 Exposure Draft baixar epub
por United States Government Accountability Office

Escolha um formato:
| zip | Baixar grátis |
|---|---|
| rar | Baixar grátis |
| epub | Baixar grátis |
| Baixar grátis | |
| lit | Baixar grátis |
| odf | Baixar grátis |
Descrição do livro
FEDERAL INFORMATION SYSTEM CONTROLS AUDIT MANUAL(FISCAM)
2023 Exposure Draft
The Federal Information System Controls Audit Manual (FISCAM) presents a methodology for assessing the design, implementation, and operating effectiveness of information system (IS) controls. Generally accepted government auditing standards (GAGAS) define IS controls as internal controls that depend on information system processing.8 IS controls include user, application, and general controls. This manual uses the term “IS controls assessment” to refer to the auditor’s assessment of IS controls using FISCAM.
This exposure draft updates the Federal Information System Controls Audit Manual (FISCAM) to reflect changes in relevant auditing standards, guidance, control criteria, and technology since the last revision. The summary of major proposed changes below focuses on those changes that meaningfully affect the FISCAM methodology and does not include minor editorial changes.
Changes to the Format, Design, and Organization
Enhance the usability of the manual. The 2023 FISCAM exposure draft proposes to reformat, redesign, and reorganize FISCAM to enhance its usability. The major proposed changes to the format include the use of numbered sections, numbered paragraphs, and subheadings. Other major proposed changes to the design and organization of the manual are discussed below.
• The 2023 FISCAM exposure draft proposes four sections that include new and existing content from chapters 1 and 2 of extant FISCAM. Section 100, Introduction, provides an overview of the FISCAM methodology. Section 200, Planning Phase, includes auditor requirements, guidance, and procedures for planning an information system (IS) controls assessment, including identifying relevant IS control objectives. Section 300, Testing Phase,includes auditor requirements, guidance, and procedures for identifying IS controls for testing and determining the nature, extent, and timing of IS control tests. Section 400,Reporting Phase, includes auditor requirements and guidance for communicating the results of the IS controls assessment.
• The 2023 FISCAM exposure draft proposes the following three appendixes included as section 500:
• Appendix 500A, FISCAM Glossary, updates extant FISCAM appendix XI, Glossary.
• Appendix 500B, FISCAM Framework, updates the tables containing critical elements,control activities, control techniques, and suggested audit procedures from extant FISCAM chapters 3 and 4.
• Appendix 500C, FISCAM Assessment Completion Checklist, provides new content that assists auditors with determining whether the FISCAM methodology was followed.
• Given the potential for revisions to address public comments, the 2023 FISCAM exposure draft does not include figures, such as those included in extant FISCAM. However, we anticipate the final product will include figures derived from the final product content. We are requesting feedback on the types of information that may be useful to provide in the form of figures.
Autores populares
Icon Group International (402) Publishing lmgdaw (341) Nikolay Krechet (266) Unknown Author (197) Lyudmil Tsvetkov (179) Barrett Williams (166) Kennie B Journals (158) Riddler Books (122) ChatGPT ChatGPT (118) NAK Legal Publishing (116) Evgeniia Naumchenko (114) Sharifa McFarlane (97) Jillo Trukudo (96) Quick Witted Coconut (94) Roggie Clark (94) Mint and Cherry Notebooks (93) Marina Buchholz B.Eng (89) Iwona Makara (87) Mary Hirose (87) Kingston Publishing (85)